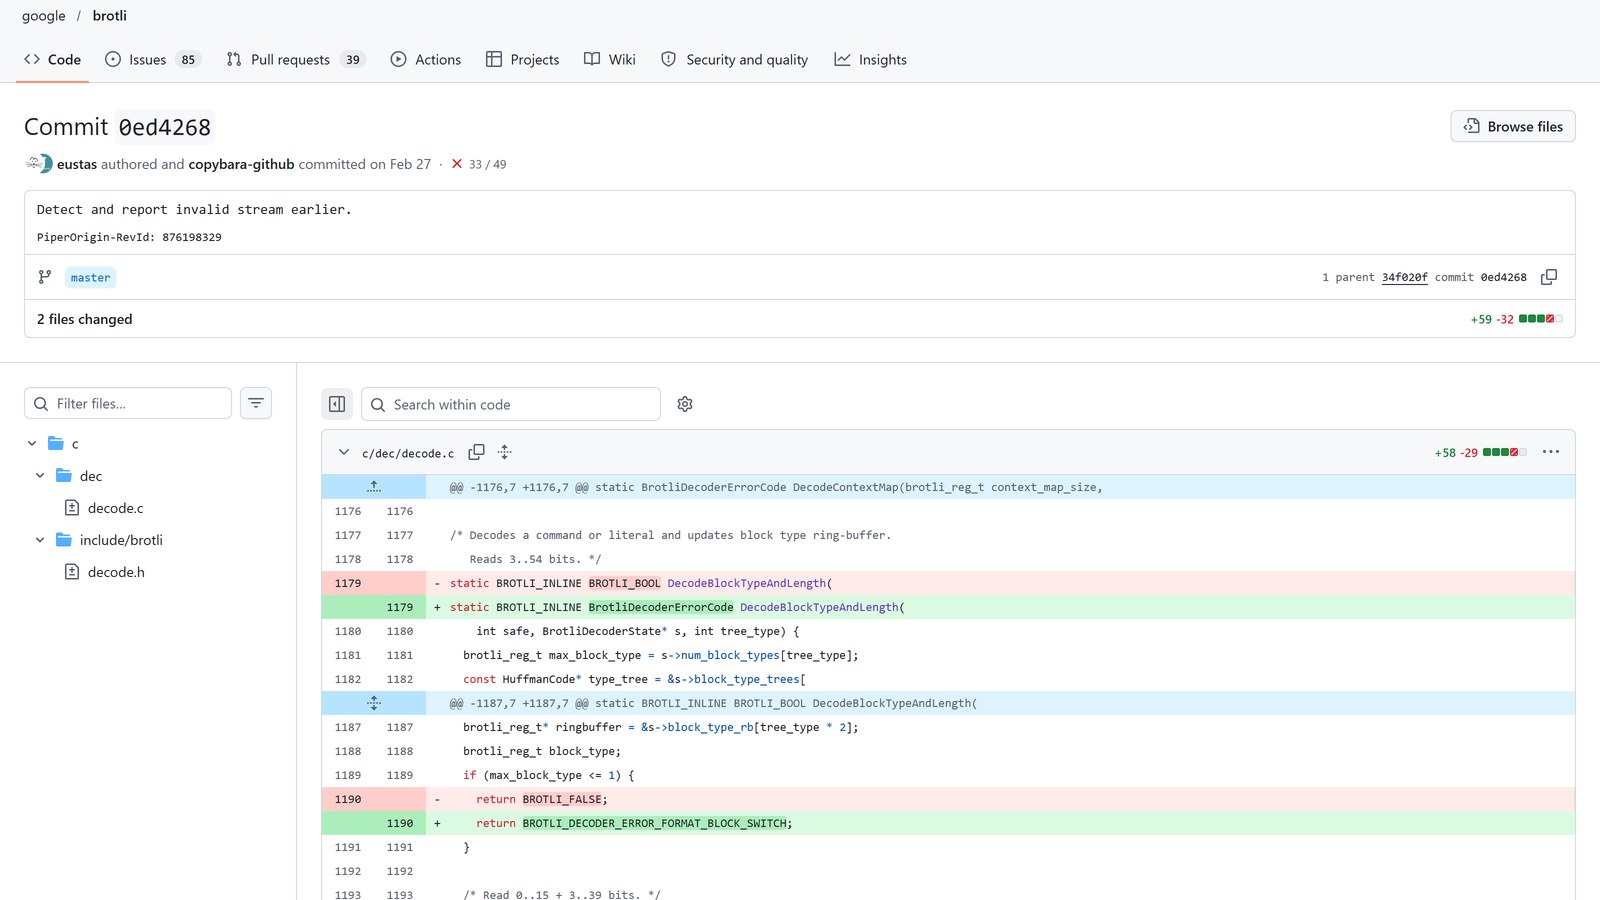
The Brotli fix shipped in February. The CVE arrived in October
CVE-2026-111497 is a 9.8 in the compression library inside every browser. The commit that fixes it was pushed to public master on 27 February and no release carried it for 236 days.
grep -rl "memory-safety" ./articles

CVE-2026-111497 is a 9.8 in the compression library inside every browser. The commit that fixes it was pushed to public master on 27 February and no release carried it for 236 days.
CVE-2026-111497 was added on 27 October with a due date of 10 November. The catalogue lists Google Brotli, and the fix arrives separately in Node, .NET, Bun, Envoy, Istio, the PHP Windows builds and your distribution's own package.
CVE-2026-111497 is an out-of-bounds write in the Brotli decoder, scored 9.2 by Google and High by Node. The exposure most people have is fetch, which decodes Brotli on the response's say-so.
The technical reason is memory management and error handling. The organisational reason is in the post-mortem, which calls the delay a structural failure. And the emergency release carried a second heap corruption nobody was looking for.