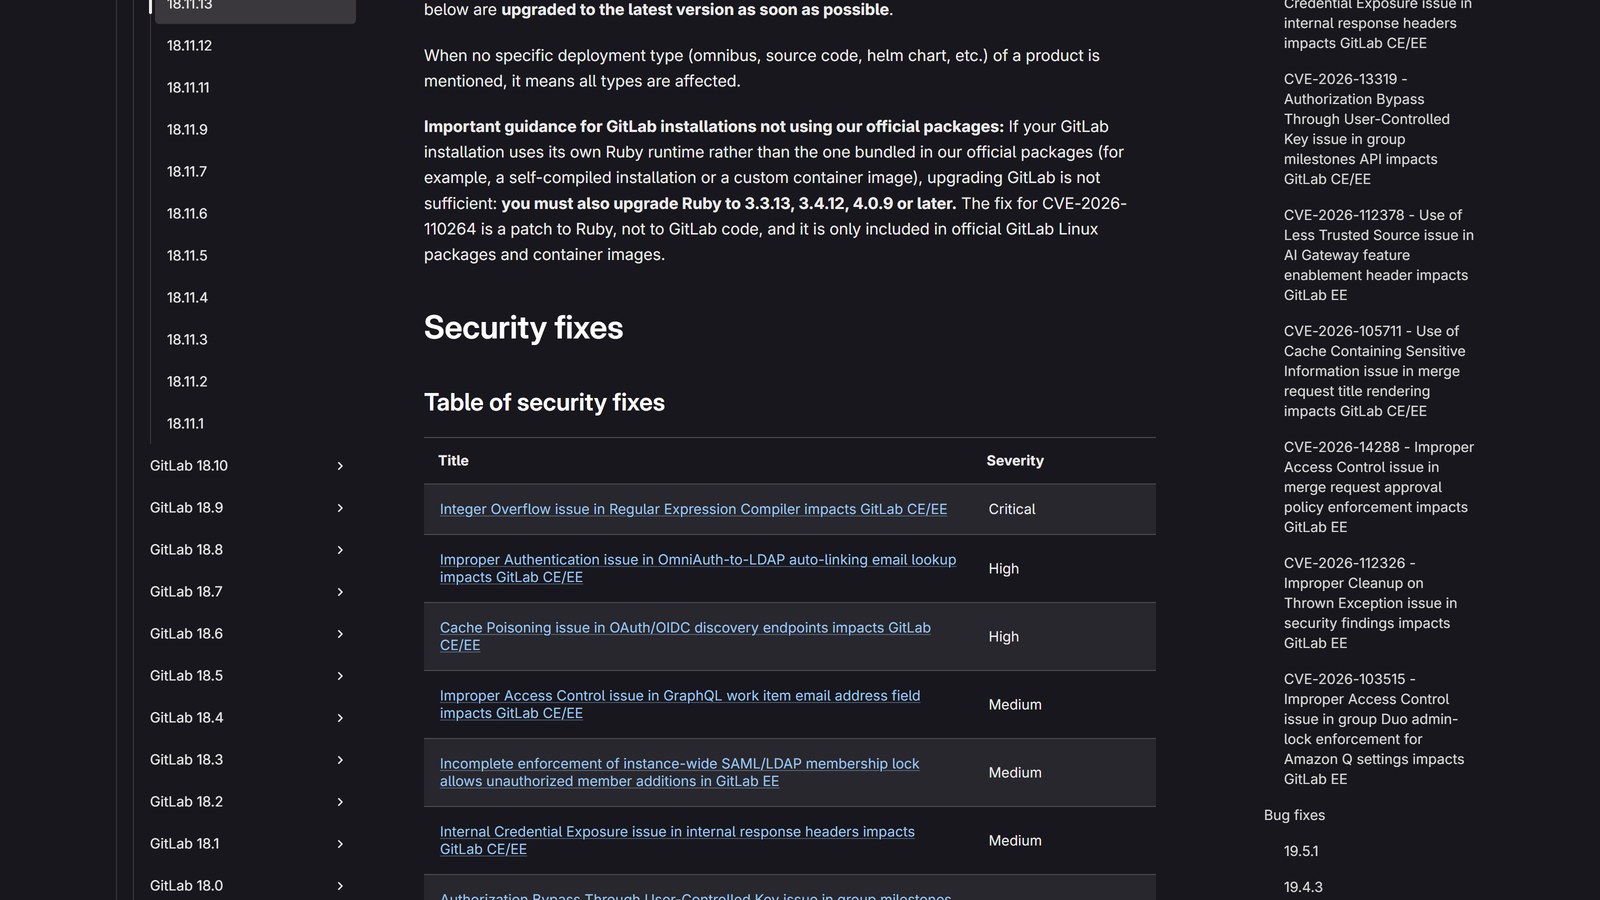
The coverage said 1,000 GitLab servers were exposed. Shadowserver's same post counted 11,300 exposed to a different bug, a CVSS 10.0 in Ruby's regex engine, and the release everyone rushed to under the CISA deadline does not contain its fix.
2 articles — 2026-10-23 to 2026-11-07
NOT IN CISA KEV — CATALOG 2026.11.06
Authoritative record
Root Notes reports on this identifier; it does not maintain it. For the vendor advisory, the affected versions and the scoring, NVD and MITRE hold the primary records.
Not listed in CISA's Known Exploited Vulnerabilities catalog as of catalog 2026.11.06. That is not evidence it is not being exploited — the catalog records what CISA has confirmed, and identifiers have been attacked for days before appearing in it.
The coverage said 1,000 GitLab servers were exposed. Shadowserver's same post counted 11,300 exposed to a different bug, a CVSS 10.0 in Ruby's regex engine, and the release everyone rushed to under the CISA deadline does not contain its fix.
CVE-2026-110264 is an integer overflow when compiling a crafted regular expression, and GitLab says it could have let an unauthenticated user run code on the server. The affected range starts at a version from 2014.